6 Open Source AI Gateways Ranked for September 2026
Most open source AI gateway comparisons focus on how many providers a tool supports. That's a fine starting point, but it misses the question that actually drives architecture decisions: what happens at the API boundary when an output is unsafe, off-policy, or audit-relevant? The answer varies a lot across tools. Here's where each of the six best options currently stands.
TLDR:
- Most open source AI gateways handle routing well; active output blocking and compliance mapping are where the field thins out fast
- Self-hosting an AI gateway keeps inference traffic off third-party infrastructure, which matters for data residency and regulated workloads
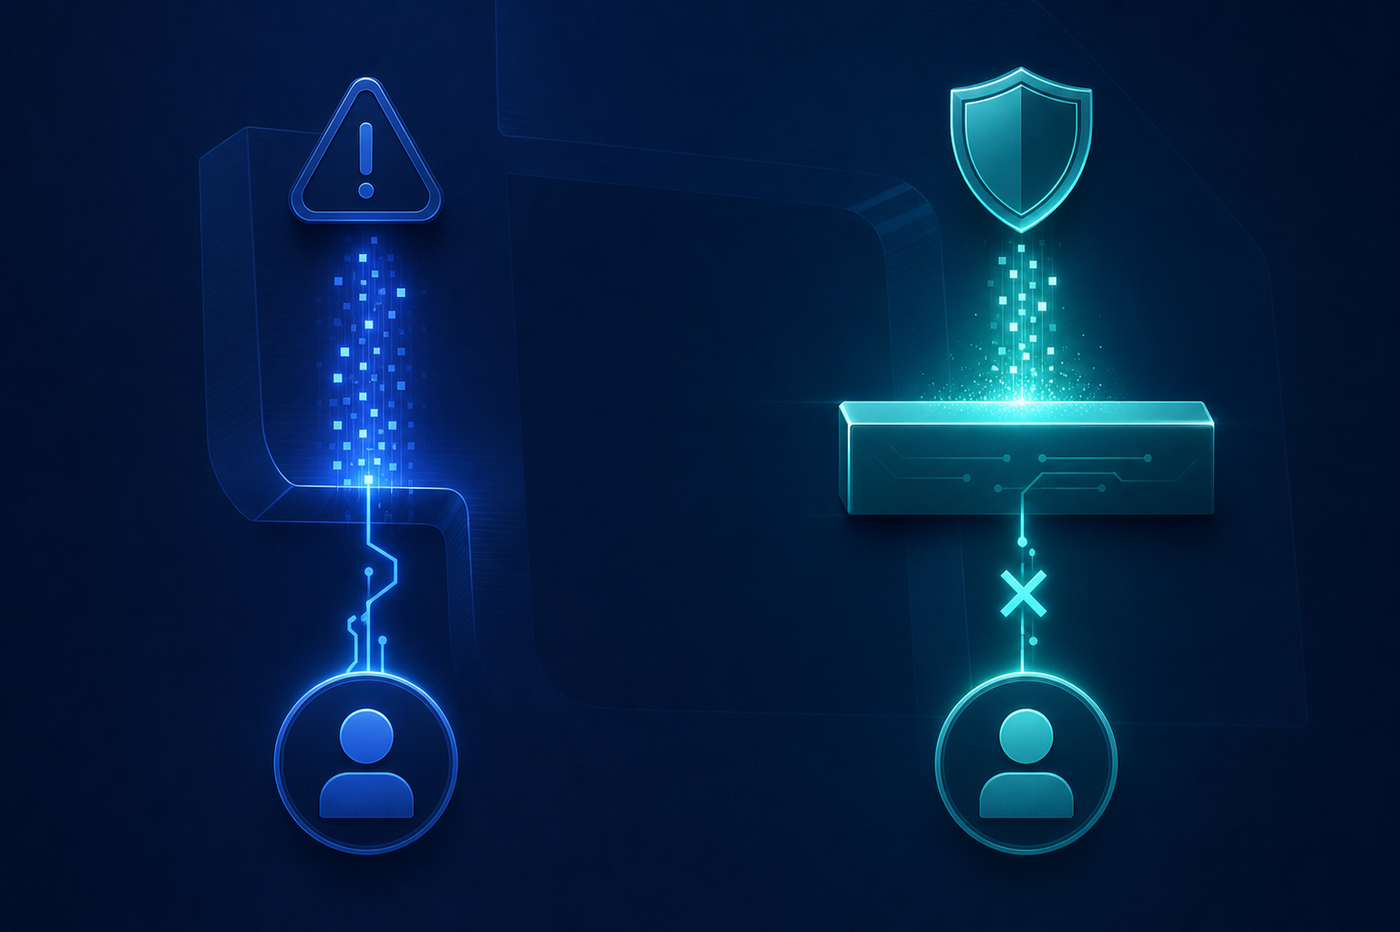
- Logging an unsafe output after it reaches a user is observation; stopping it before it exits the API boundary is enforcement, and few tools do the latter
- LiteLLM, Bifrost, Kong, APISIX, and Helicone each cover routing but currently stop short of behavioral evaluation, CI/CD gates, or automated compliance mapping
- Openlayer is the only option in this comparison that operates across routing, real-time output guardrails, over 175 pre-built tests, and automated EU AI Act and NIST AI RMF mapping
What is an open source AI gateway?
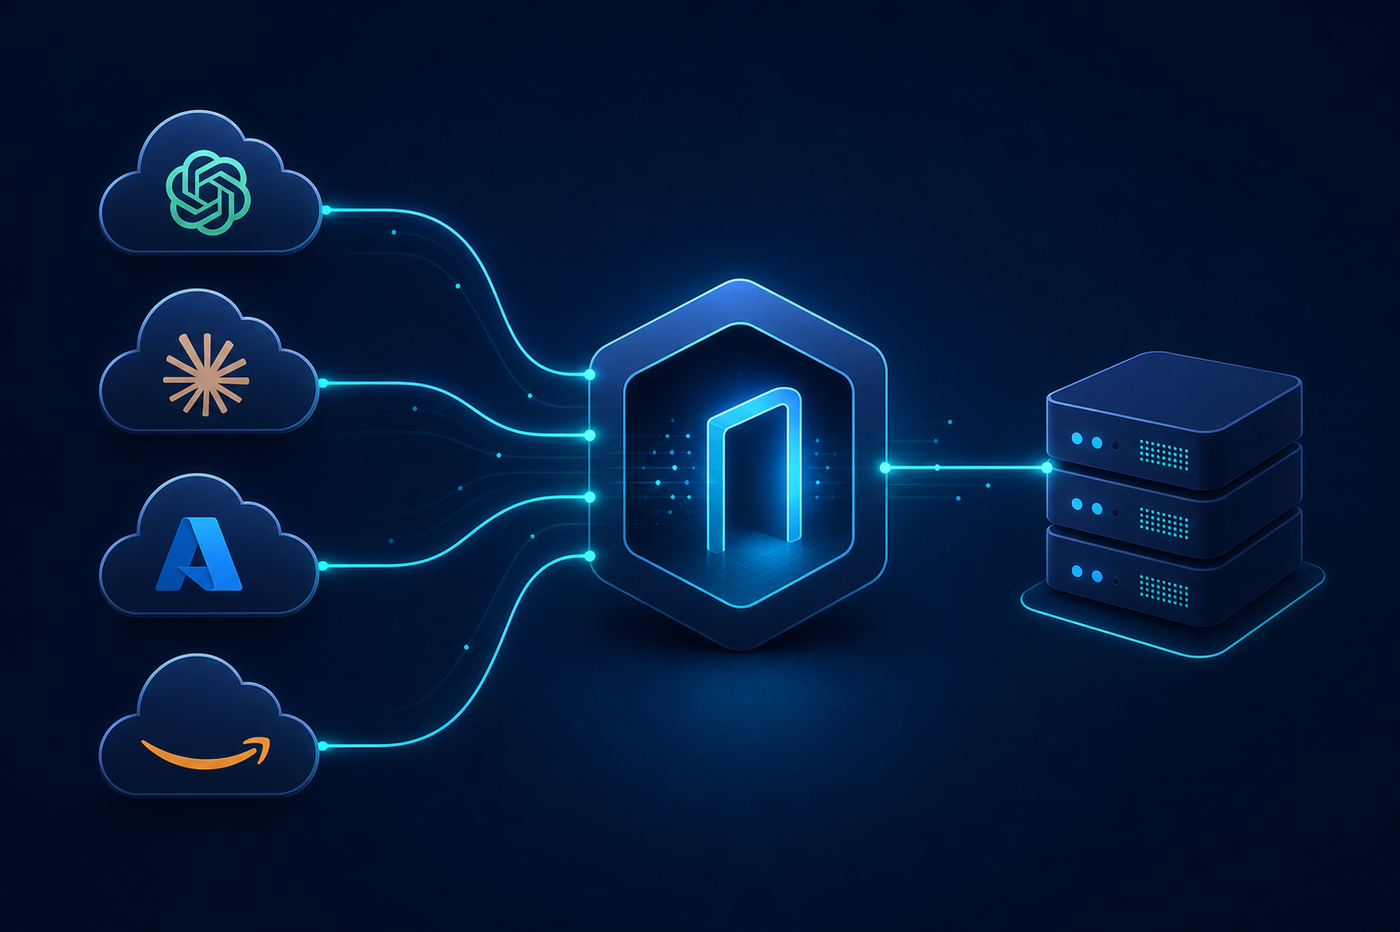
An open source AI gateway is a self-hosted layer that sits between your application and the LLM providers you call: OpenAI, Anthropic, Azure, Bedrock, and others. Instead of building provider-specific logic into every service, you route all inference traffic through a single control point that handles the common concerns: request routing, fallback logic, rate limiting, cost tracking, and authentication.
The "open source" part matters for a specific reason. Managed gateways are convenient, but every request passes through someone else's infrastructure. For teams operating under data residency requirements, handling regulated data, or running at scale where per-request fees compound fast, self-hosting is the practical path.
At a functional level, a gateway does four things:
- Routes requests to the right provider or model based on cost, latency, or availability rules
- Falls back to an alternate provider when the primary one is unavailable or throttling
- Tracks spend and enforces budget limits across teams and API keys
- Exposes a unified API so your application code stays stable when you swap underlying models
The tools in this list vary widely in scope. Some stop at routing and cost control. Others add observability, guardrails, and compliance controls on top. Which capabilities matter depends on where your stack is today and what production actually requires.
How we ranked these open source AI gateways
Each gateway on this list was assessed on the same criteria, drawn from publicly available documentation, GitHub repositories, and benchmarks.
- Provider breadth: How many LLM providers does it support, and how cleanly does it handle the differences between them?
- Latency and throughput: What overhead does the gateway add under load? For high-volume deployments, this is often the deciding factor.
- LLM observability: Does it surface cost, latency, and usage data natively, or do you need to wire up a separate monitoring stack?
- Enforcement and guardrails: Can it actively block unsafe outputs, or does it only log them?
- Compliance and governance: Does it map to regulatory frameworks, generate audit evidence, or support policy-as-code?
- Deployment flexibility: Self-hosted, managed cloud, air-gapped, or all three?
- Integration ecosystem: How well does it fit into existing dev workflows, including CI/CD, agent frameworks, and enterprise conversational platforms?
Most open source gateways handle the first two well. Fewer handle observability with any depth. Almost none cross from detection into active enforcement. That gap matters more as AI systems move from chatbots into agents taking real actions, and it's the primary lens applied here.
Best overall open source AI gateway: Openlayer
Most open source AI gateways stop at routing. Openlayer starts there and goes further, into active enforcement, evaluation, and automated compliance.
The managed LLM Gateway handles centralized routing across OpenAI, Anthropic, Azure, and OpenRouter, with per-API-key spending limits, projected cost savings visibility, and budget controls that enforce at the team and key level. That's the baseline. What separates Openlayer is what happens at the API boundary before a response exits.
Real-time guardrails block prompt injections, PII leakage, toxic content, and unauthorized tool calls using a five-action enforcement taxonomy: allow with logging, warn, block, redact, or escalate to a human reviewer. Logging an unsafe output after it reaches a user is observation. Stopping it before it exits the API boundary is runtime AI enforcement. Openlayer operates in the second category.
Beyond routing and guardrails, Openlayer includes over 175 pre-built automated tests, LLM-as-a-judge evaluation at 81.3% human correlation, and CI/CD deployment gates that block builds when thresholds fail. Compliance mapping to EU AI Act, NIST AI RMF, ISO 42001, and AIUC-1 is automated, with per-request audit records generated as a byproduct of enforcement, not assembled after the fact.
SDKs ship in Python, TypeScript, Java, and Go. Native integrations cover Salesforce Agentforce, Microsoft Copilot Studio, Google Dialogflow, LangChain, LangGraph, and the Anthropic Claude Agent SDK.
Best for: organizations deploying AI in regulated or high-stakes environments where a routing proxy alone creates compliance exposure.
LiteLLM
LiteLLM offers a unified OpenAI-compatible interface to 100+ LLM providers, handling routing, retries, fallback, and per-project spend tracking through a self-hosted proxy server.
- Unified API across 100+ providers with standardized input/output format
- Router with retry and fallback logic across deployments
- Per-project budget tracking via proxy server
- Docker-based self-hosting with a Python SDK
Community reports cite cost reductions of up to 56% from LiteLLM deployments at scale, which signals its strength in routing and cost management. With 57.6k GitHub stars, the ecosystem is mature and well-documented.
The gap is at the enforcement and governance layer. LiteLLM logs and routes; it does not block unsafe outputs, run pre-deployment evaluations, or map results to EU AI Act or NIST AI RMF obligations. Teams needing audit evidence from LLM traces must build those layers separately.
Best for: Engineering teams focused on provider breadth and self-hosted cost tracking without a compliance mandate.
Bottom line: Strong routing proxy. Organizations needing runtime enforcement or regulatory evidence will need to supplement it.
Bifrost
Bifrost is a Go-based open source AI gateway built for throughput. In independent benchmarks, it adds only 11 microseconds of overhead at 5,000 requests per second, a performance ceiling Python-based gateways can't match.
- 11 µs added latency at 5,000 RPS
- Unified access to 20+ providers including OpenAI, Anthropic, AWS Bedrock, Google Vertex, and Azure
- Automatic failover, load balancing, and semantic caching out of the box
- Drop-in replacement by changing only the base URL, with no code refactor required
The GitHub repository has 7.7k stars, reflecting genuine traction among performance-focused teams. Where Bifrost currently stops: there is no behavioral evaluation, no LLM-as-a-judge scoring, no compliance framework mapping, and no active guardrails blocking unsafe outputs before they reach users. It is a routing and performance layer, not a governance one.
Best for: high-volume production workloads where raw throughput is the primary constraint.
Bottom line: Strong throughput-first routing layer. Teams operating under compliance obligations will need to build the enforcement and audit layers separately.
Kong AI Gateway
Kong AI Gateway sits on top of the open source Kong Gateway, which has 44.1k GitHub stars, with AI-specific plugins layered on for LLM traffic routing, rate limiting, and observability.
What They Offer
- AI-specific plugins for multi-provider LLM routing and rate limiting
- MCP and Agent2Agent protocol support for agent infrastructure
- 100+ gateway plugins covering authentication, traffic control, and observability
- Self-hosted and managed (Kong Konnect) deployment options
Best for: Teams already running Kong for API management who want to extend their existing gateway to handle LLM traffic without adopting a separate tool.
Limitation: Kong's AI governance scope is currently API-level traffic control. There is no LLM-as-a-judge scoring, no pre-built safety or compliance test library, no automated mapping to EU AI Act or NIST AI RMF, and no CI/CD deployment gates that block builds when behavioral thresholds fail.
Bottom line: A natural extension for Kong-native teams. Organizations that need behavioral evaluation, output enforcement, or automated compliance evidence generation will find those capabilities outside Kong's current scope.
Apache APISIX
Apache APISIX is an Apache 2.0-licensed open source API and AI gateway built on a plugin architecture, routing traffic to 20+ LLM providers including OpenAI, Anthropic, AWS Bedrock, DeepSeek, and Ollama. It adds 0.2 ms of latency at approximately 18,000 QPS per core.
What They Offer
- Multi-LLM proxy routing with load balancing, retries, and fallback across providers
- Token rate limiting, prompt policy enforcement, and basic moderation via open source AI plugins
- 100+ gateway plugins spanning authentication, traffic control, and observability
- Portable configuration with no vendor lock-in; 17.1k GitHub stars
Best for: Teams already running APISIX for microservices who want to unify API and LLM traffic under one high-performance gateway without adopting a separate tool.
Limitation: The AI plugin ecosystem currently covers routing and token controls but stops there. No pre-built LLM behavioral evaluation, no LLM-as-a-judge scoring, no automated mapping to EU AI Act or NIST AI RMF, and no active guardrails generating per-request audit trails.
Bottom line: A strong fit for cloud-native infrastructure teams adding LLM routing with minimal latency overhead. Regulated teams needing behavioral governance or audit-ready compliance evidence will need to add those layers elsewhere.
Helicone
Helicone is an open source AI observability and gateway platform with 6.2k GitHub stars on the main helicone/helicone repository (the standalone ai-gateway sub-repo carries 626 stars separately). It provides unified API access to 100+ LLM providers through the OpenAI SDK format, with built-in observability and cost tracking. Note: Helicone was acquired by Mintlify in March 2026; its development roadmap may shift under new ownership.
What They Offer
- Unified API across 100+ LLM providers with no markup on credits and automatic provider failover
- Request logging, prompt management, and usage analytics in a single dashboard
- Self-hosted and cloud-hosted deployment options
Best for: Developer teams who need lightweight observability and provider routing with low integration friction.
Limitation: Helicone currently covers routing and logging. It does not include behavioral evaluation, LLM-as-a-judge scoring, compliance mapping to EU AI Act or NIST AI RMF, or active guardrails that block unsafe outputs before they exit the API boundary.
Bottom line: Solid developer-facing observability tool. Teams that need output enforcement or regulatory audit trails require a tool with broader governance scope.
Feature comparison table of open source AI gateways
The table below maps seven capabilities across the six tools covered in this post. Routing and cost tracking appear in several options, but active output guardrails, evaluation, and compliance mapping are where the field thins out fast.
| Capability | Openlayer | LiteLLM | Bifrost | Kong | APISIX | Helicone |
|---|---|---|---|---|---|---|
| Multi-Provider LLM Routing | Yes | Yes | Yes | Yes | Yes | Yes |
| Built-in Cost Tracking | Yes | Yes | Yes | No | No | Yes |
| Active Output Guardrails (Blocking) | Yes | No | No | No | No | No |
| Pre-Built Evaluation Tests | Yes | No | No | No | No | No |
| LLM-as-a-Judge Scoring | Yes | No | No | No | No | No |
| Automated Compliance Mapping (EU AI Act / NIST) | Yes | No | No | No | No | No |
| CI/CD Deployment Gates | Yes | No | No | No | No | No |
Why Openlayer is the best open source AI gateway
Routing gets requests to the right model. It does not stop a hallucinating response from reaching a user. It does not block a prompt injection in an agentic pipeline. It does not produce the audit record an EU AI Act conformity assessment requires. Every other tool in this comparison handles routing well. Some add cost tracking or basic observability. None cross from alerting into active enforcement, and that gap is where compliance exposure is made.
Openlayer is the only option here that operates across the full control plane: unified LLM routing, real-time output guardrails that block before responses exit the API boundary, over 175 pre-built behavioral evaluation tests, and automated mapping to EU AI Act, NIST AI RMF, and ISO 42001. Continuous compliance evidence is generated as a byproduct of enforcement at inference time, not assembled after the fact from logs.
For teams without regulatory exposure, a routing proxy is often enough. For teams in financial services, healthcare, or any deployment subject to EU AI Act high-risk system obligations, the distance between a routing gateway and an enforcement gateway is precisely where audit findings get made. A compliance gap is not a logging problem; it is a control problem. Openlayer covers both.
Final thoughts on open source AI gateway options
For a lot of teams, a routing proxy with cost tracking is genuinely sufficient. But if your deployment touches regulated data, high-risk decisions, or agent pipelines where a bad output causes real harm, observation alone isn't a control. The distance between logging an unsafe output and blocking it is where compliance exposure lives. Connect with the Openlayer team to see what enforcement looks like in practice.
FAQ
How do I choose the right open source AI gateway for my team's needs?
Start with your compliance posture. If your deployment has no regulatory exposure, a routing proxy like LiteLLM or Bifrost handles provider breadth and cost tracking well. If you operate under EU AI Act high-risk system obligations, NIST AI RMF, or similar frameworks, you need a gateway that crosses from detection into active enforcement: one that blocks unsafe outputs before they exit the API boundary and generates audit records as a byproduct of that enforcement, not assembled after the fact.
Is Bifrost or LiteLLM better for high-throughput production workloads?
Bifrost is the stronger choice for raw throughput, adding only 11 microseconds of overhead at 5,000 requests per second, a ceiling Python-based gateways like LiteLLM cannot match. LiteLLM compensates with broader provider coverage (100+ providers) and more mature cost tracking. Neither includes behavioral evaluation, compliance mapping, or active output guardrails, so teams with governance requirements will need to build those layers separately regardless of which they choose.
What is the difference between an AI gateway that logs unsafe outputs and one that blocks them?
The distinction is covered above: logging means the unsafe output has already reached a user before anyone can intervene, while blocking at the API boundary stops it before it exits. For agentic systems where a tool call can execute a database write or external API call in milliseconds, the gap between those two positions is where regulatory liability and irreversible production events are made.
When should I consider Openlayer over a standalone routing gateway like Kong AI Gateway or Apache APISIX?
Kong and APISIX are well-suited for teams already running those gateways for API management who want to extend LLM traffic routing without adopting a separate tool. The gap appears at the behavioral layer: neither includes LLM-as-a-judge scoring, pre-built safety test libraries, CI/CD deployment gates that block builds on threshold failure, or automated mapping to EU AI Act or NIST AI RMF. If your deployment requires audit-ready compliance evidence or runtime output enforcement, those capabilities sit outside both tools' current scope.
Can any of these open source AI gateways satisfy EU AI Act high-risk system obligations on their own?
No single tool on this list satisfies EU AI Act high-risk system obligations on its own, as compliance is a shared organizational responsibility. Among the gateways compared here, Openlayer is the only one that generates per-request audit records at inference time, maps evaluation results to specific EU AI Act articles (Articles 9 and 15, which cover risk management and accuracy/robustness respectively), and blocks non-compliant outputs before they reach users. The other gateways handle routing and, in some cases, logging, but produce none of the structured compliance evidence an Article 43 conformity assessment procedure requires.