Enterprise AI Regulatory Compliance Explained (October 2026)
In February 2023, Derek Mobley sued Workday in the U.S. District Court for the Northern District of California, alleging that the vendor's algorithmic applicant-screening tools let employers discriminate against Black applicants, applicants over 40, and applicants with disabilities. This is exactly the kind of failure AI regulatory compliance is designed to catch and govern: when a court or regulator asks whether a hiring screen treated protected groups fairly, a policy stating the model "will not discriminate" is not an answer. Demographic parity records, evaluation results, and monitoring logs showing the controls were active are, and the EU AI Act classifies hiring screens as high-risk systems under Annex III. (AI Incident Database, Incident #489, https://incidentdatabase.ai/cite/489/)
TLDR:
- AI regulatory compliance requires evidentiary proof that controls were active, not policy documents stating they should be.
- 88% of organizations deployed AI in 2025, but fewer than 25% have fully implemented bias, transparency, and security controls.
- EU AI Act high-risk systems face an August 2026 enforcement deadline covering risk management, bias testing, and incident reporting within 15 days.
- Logging records what happened after harm occurs; only blocking at the API boundary constitutes actual enforcement under Articles 9 and 14.
- Openlayer covers the full compliance lifecycle, with CI/CD gates that block deployment when groundedness falls below 85% or demographic parity gaps exceed 5 percentage points.
What AI regulatory compliance means in 2026
AI regulatory compliance means proving that your AI systems behave within defined legal and ethical boundaries, beyond merely documenting that they should.
Traditional software compliance means audit logs, access controls, and data handling records. AI compliance requires something structurally different: evidence that a model's outputs are accurate, fair, safe, and traceable across its entire active life. A policy document stating your model "will not discriminate" satisfies no regulator. The evidence that it didn't, including demographic parity records, evaluation results, and drift monitoring logs, is what compliance actually requires.
The scope runs the full lifecycle: pre-deployment evaluation against safety and fairness criteria, continuous production monitoring for behavioral drift, real-time controls that block unsafe outputs, and audit trails that can reconstruct what a model did at inference time. Regulators reviewing a high-risk system under the EU AI Act aren't asking whether you have a governance policy; they're asking for the evidentiary record that your controls were active, not assembled after an incident.
The adoption vs. governance gap enterprises face
Aon data shows 88% of organizations used AI in at least one business function in 2025, yet Economist Impact research found that only 8% of those organizations maintain a governance framework to match. That gap between deployment and oversight is where most enterprises actually live.
The self-reporting numbers make it worse. IBM data shows 87% of organizations claim clear AI governance frameworks, but fewer than 25% have fully implemented the controls needed to manage bias, transparency, and security risks. Claiming governance and running governance are two different things, and regulators are beginning to treat that difference as a liability.
The global AI regulatory environment
Two categories shape what enterprises actually owe regulators: binding law with enforcement deadlines, and voluntary frameworks that define what "adequate" governance looks like when an auditor arrives.
Binding regulations
- The EU AI Act is the world's first broad-scope horizontal AI regulation, enforceable from August 2026 for high-risk systems. It applies to any provider or deployer whose systems are used in the EU, regardless of where that organization is headquartered.
- GDPR intersects with AI wherever personal data drives model inputs or outputs. Automated decision-making under Article 22 carries disclosure and contestation obligations on top of any AI Act requirements.
- The UK has diverged post-Brexit, issuing a principles-based framework through the AI Safety Institute instead of a single binding statute. Sector regulators (FCA, ICO, CQC) are folding AI expectations into existing supervisory frameworks.
Voluntary frameworks that shape audit expectations
- NIST AI RMF organizes governance around four functions: Govern, Map, Measure, and Manage. Voluntary in the US, but regulators and procurement requirements increasingly treat it as the baseline for responsible AI practice.
- ISO 42001 is the international standard for AI management systems. Organizations with existing ISO 27001 certification can reach ISO 42001 compliance up to 40% faster, making it a cost-effective extension for enterprises already inside the ISO ecosystem.
Geographic headquarters determines very little. If a model serves EU users, EU AI Act obligations attach. If it processes personal data, GDPR applies. If it operates in a regulated sector, sector-specific requirements layer on top.
How the EU AI Act risk classification works
The EU AI Act sorts AI systems into four tiers, and which tier a system lands in determines everything about compliance obligations.
| Risk Tier | Enforcement Date | Example |
|---|---|---|
| Unacceptable (prohibited) | February 2025 | Social scoring systems by public authorities |
| High-risk (Annex III) | August 2026 | Credit scoring, hiring screening, benefits eligibility |
| Limited risk | August 2024 | Chatbots requiring user disclosure |
| Minimal risk | No binding obligations | Spam filters, AI-assisted grammar tools |
Prohibited practices have been off the table since February 2025: biometric categorization systems that infer sensitive characteristics, real-time remote biometric surveillance in public spaces, and government social scoring. Violations carry fines up to €35 million or 7% of global annual turnover under Article 99(6).
High-risk AI systems are where most enterprises are focused. The August 2, 2026 enforcement date covers Articles 9 through 17 for providers and Article 26 for deployers: risk management, data governance, technical documentation, logging, human oversight, and accuracy. A credit scoring model, an AI resume screener, an insurance underwriting engine: all fall under Annex III. Non-compliance carries fines up to €15 million or 3% of global annual turnover under Article 99(3).
GPAI providers have faced technical documentation and transparency obligations since August 2025; these are already in force, distinct from the August 2026 deadline applying to high-risk systems. Models with systemic risk (training compute exceeding roughly 10²⁵ FLOPs) carry additional requirements: adversarial testing, incident reporting to the EU AI Office, and published training data summaries.
Specific obligations for high-risk AI systems
Four articles do the real work for high-risk systems, each imposing a specific, ongoing compliance burden.
- Article 9: Continuous risk management: A living risk management system, not a pre-deployment sign-off. Risks must be reassessed as inputs shift, user populations expand, or regulatory scope changes. In practice: a credit scoring model serving a new geographic market triggers a re-review, with documented demographic parity test results attached before the expansion goes live.
- Article 10: Data governance and bias testing: Training data must be reviewed for representativeness, and bias testing must run across demographic subpopulations before deployment. In practice: an insurance underwriting model requires documented assessment of approval rate gaps across protected classes, with any gap exceeding 5 percentage points flagged for review before promotion.
- Article 15: Ongoing accuracy and adversarial robustness: Accuracy measurement continues after deployment, and adversarial robustness testing including prompt injection and jailbreak resistance is a named requirement. In practice: a benefits eligibility system runs monthly groundedness and adversarial prompt evaluations, with results logged as audit evidence under Article 43 conformity assessment records.
- Articles 61 and 72: Post-market monitoring and incident reporting: Production behavior must be monitored continuously, with serious incidents reported to national authorities within 15 days. In practice: a hiring screen with daily drift detection triggers a High-severity review when demographic parity gaps widen beyond approved thresholds, with the investigation record attached before the alert closes.
Industry-specific compliance obligations
Regulated industries face multiple compliance regimes simultaneously, with each framework's obligations stacking on top of the others.
Financial services
Credit scoring, fraud detection, and insurance pricing are all Annex III high-risk use cases under the EU AI Act, with the August 2026 enforcement deadline in force. In the US, the NAIC Model Bulletin on AI use in insurance requires four parallel controls: an AI system inventory available on demand, named accountability per system, unfair discrimination testing with documented demographic parity thresholds, and ongoing post-deployment performance monitoring. An insurer operating across both jurisdictions runs both programs with no shared documentation format and no consolidated audit trail by default.
Healthcare
Clinical decision support tools and patient risk scoring systems sit in Annex III. HIPAA governs data handling at every stage of the model lifecycle. Under both FCRA and GDPR, adverse decisions based on automated processing require meaningful explanation: feature-level attribution a clinician or regulator can interrogate. That's a hard evidentiary requirement, not a best practice.
Public sector
Employment decisions and benefits eligibility determinations are explicitly named in Annex III. These systems affect protected classes at scale, making EEOC adverse impact standards a live US obligation alongside EU Article 10 bias testing requirements. A public-sector deployer running a hiring screen can face EU fairness documentation obligations, EEOC four-fifths rule compliance, and state-level algorithmic accountability laws, and sometimes all three apply to a single model.
The enforcement range: from documentation to active control
Compliance posture is not binary. There's a continuum between "we have a policy" and "we prevented the harm," and where an organization sits on that continuum determines its actual liability exposure.
Four positions define that continuum:
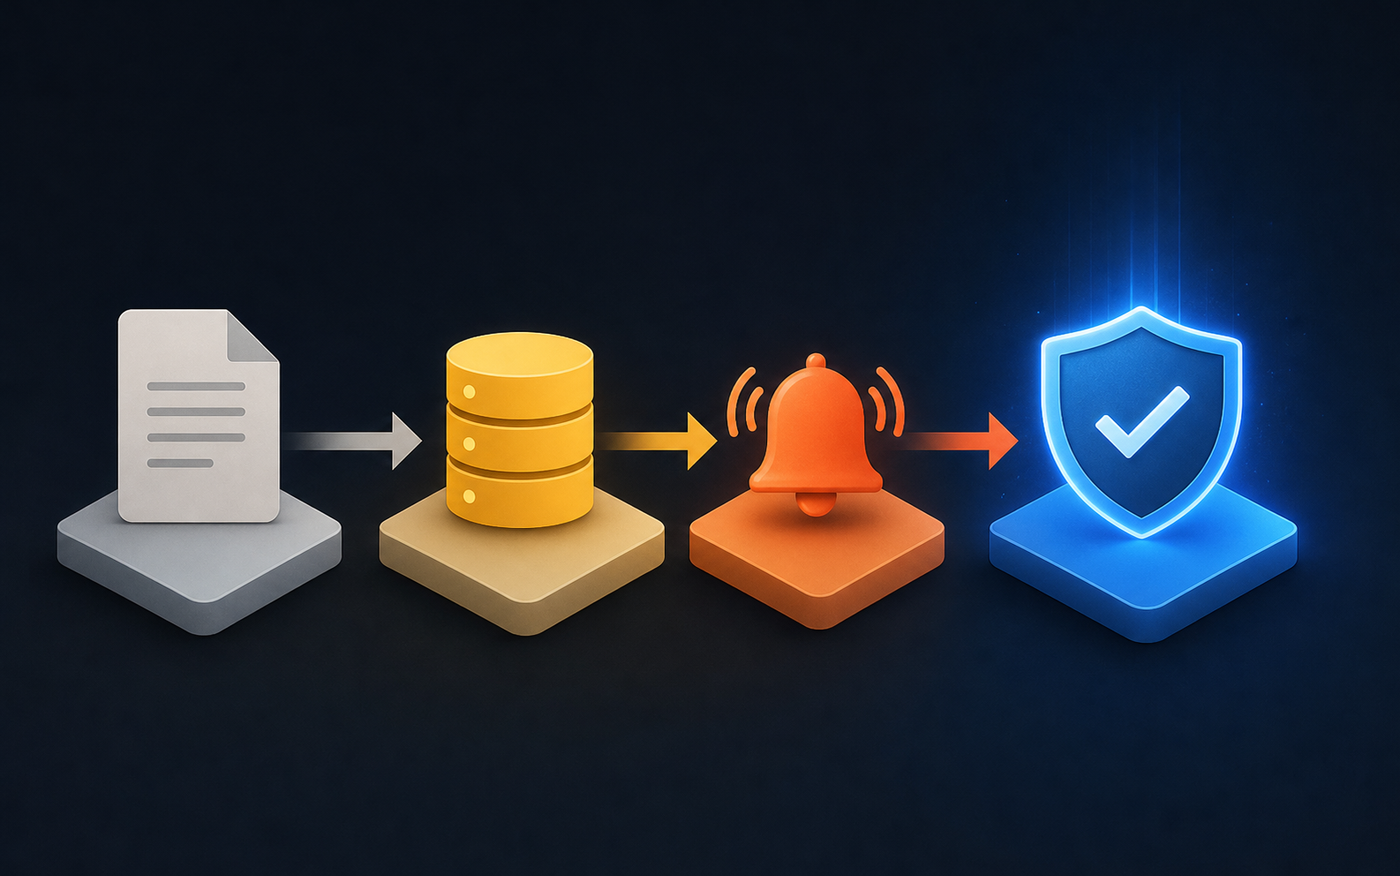
- Documentation means policies exist on paper: an acceptable use policy, a model card, a risk assessment. None of this prevents an unsafe output from reaching a user.
- Logging means inference events are recorded after the fact. When something goes wrong, you have a record. The incident has already occurred.
- Alerting means threshold breaches trigger notifications. A reviewer learns about the problem, often hours after the affected outputs were delivered.
- Blocking means unsafe outputs are stopped at the API boundary before they reach end users or downstream systems. The incident does not occur.
Every position left of blocking means a harmful output has already escaped before any intervention was possible. That's where regulatory exposure is made.
EU AI Act Article 9 requires an active risk management system, not documentation of one. Article 14 requires that human oversight measures be technically implemented to allow intervention before harm occurs. A logging setup satisfies neither: it records what happened, not in time to stop it. An audit trail of incidents that could have been blocked is not evidence of adequate control. It is evidence of a control gap.
For agentic systems, the distance between alerting and blocking becomes irreversible. When an agent fires a tool call, the downstream action executes before any post-hoc reviewer sees the log. There is no rollback path for most of those actions. The only intervention that constitutes control is one that occurs before execution, not after.
Practical challenges in building an AI compliance program
Four recurring barriers consistently stall AI compliance programs before they reach audit-readiness.
The first is inventory. Most enterprises uncover shadow AI systems only when something goes wrong. A data science team pushes a fine-tuned model without registering it. A product team connects a third-party LLM API under deadline pressure with no risk review. A business unit adopts an off-the-shelf generative tool that processes regulated data before legal learns it exists. A model running for months with no behavioral baseline cannot satisfy EU AI Act Article 9 risk management requirements retroactively, a gap a structured EU AI Act compliance checklist is designed to catch early.
The second is the manual mapping burden. Translating model evaluation results into regulatory evidence consumes 40+ hours per compliance cycle when done by hand. When an auditor asks which tests ran against a model before deployment and what the results showed, assembling that record from disconnected sources is not a compliance program. It is an incident response.
The third is scope. EU AI Act Article 4 requires that both providers and deployers confirm anyone operating or interacting with AI systems has sufficient AI literacy to understand what the system does, recognize its limits, and interpret its outputs in context. That obligation extends well past ML engineers to business analysts, customer service teams, and front-line staff.
The fourth is coordination. A high-risk system deployment requires sign-off from legal, security, data science, and business owners, often without a shared workflow to manage it. When a model update triggers a re-review under Article 9, the coordination overhead starts again from scratch.
Key AI compliance frameworks and standards
Three frameworks define what "adequate" AI governance looks like when an auditor or regulator reviews your program.
- NIST AI RMF organizes governance across four functions: Govern, Map, Measure, and Manage. Voluntary in the US, but procurement requirements and sector regulators increasingly treat it as a baseline. As of April 2026, NIST is revising the framework as part of the White House AI Action Plan, and teams building out a NIST AI RMF implementation should track those changes. The output is documented evidence of a repeatable governance process, not a certificate.
- ISO 42001 is the first international AI management system standard and, unlike NIST AI RMF, it is certifiable. An accredited third party audits your program and issues a certificate that carries weight in procurement and regulatory contexts. Organizations already holding ISO 27001 can reach ISO 42001 compliance faster, since the management system infrastructure transfers directly.
- ISO 27001 underpins many AI governance programs without being AI-specific. Encryption controls, access management, incident response, and vendor risk assessments it requires are prerequisites for AI governance, not alternatives to it.
- GPAI Code of Practice is the EU AI Act's voluntary implementation path for general-purpose AI providers subject to Article 53 obligations, signaling compliance intent while formal enforcement guidance matures.
ISO 42001 produces a certificate an auditor can inspect; NIST AI RMF produces a documented process. Procurement and due diligence favor the certificate; regulatory conversations favor the process depth.
Building an AI compliance program: core components
Five components make an AI compliance program defensible. Miss any one and the program has a structural gap auditors will find.
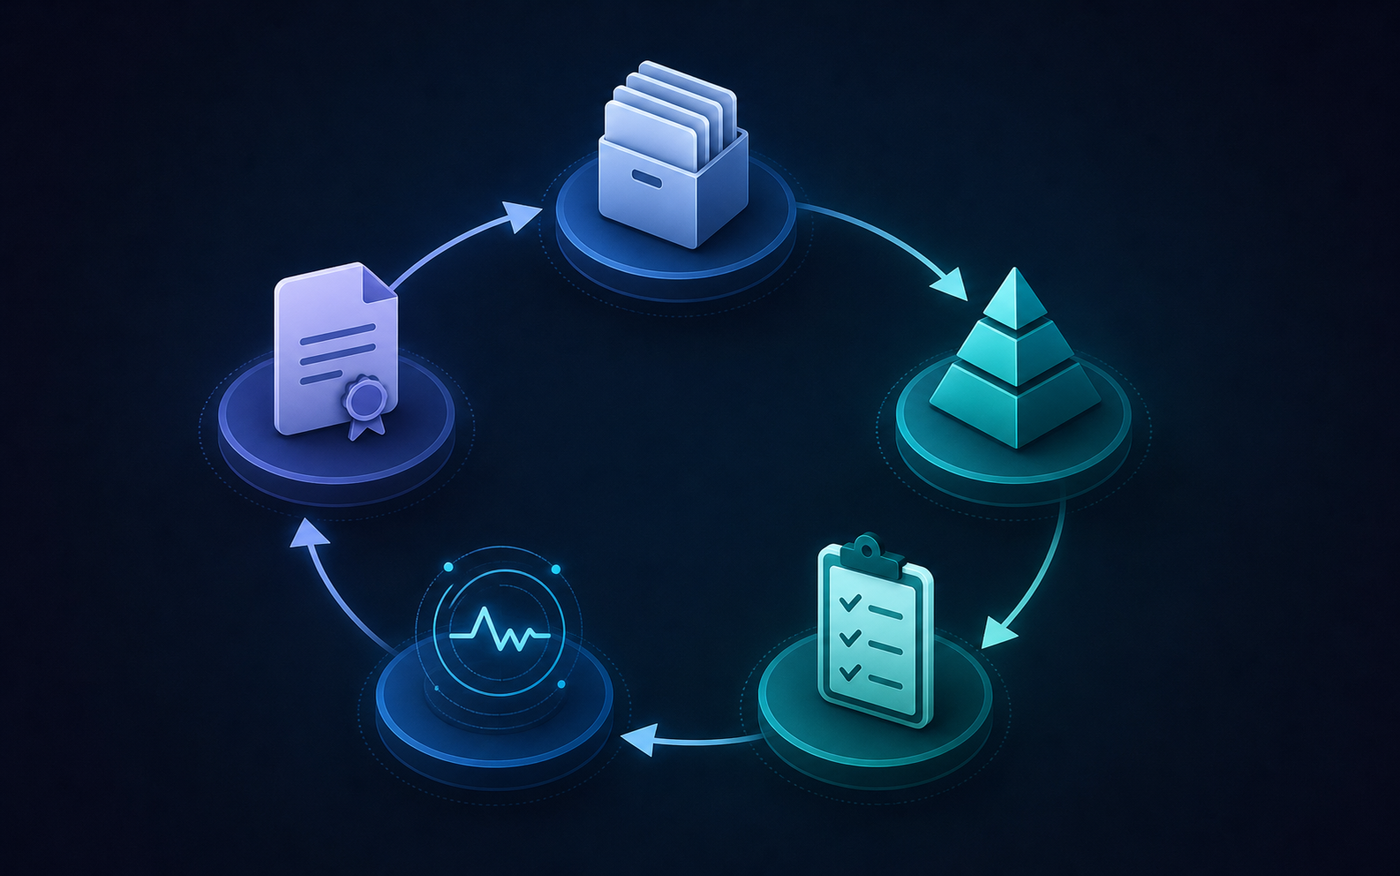
1. AI system inventory and registration
You cannot govern what you cannot see. Unregistered models cannot be monitored for drift, mapped to regulatory obligations, or pulled from production when a failure surfaces. Every registered system needs named ownership, a risk tier, model version, intended use, and a monitoring status an auditor can inspect without ambiguity.
2. Risk classification and tiering
Not every model warrants the same controls. Multi-dimensional scoring across impact scope, failure severity, observability, and regulatory exposure produces a composite score that drives proportionate governance: higher-risk systems trigger more stringent evaluation gates, more frequent monitoring, and more sign-offs before promotion.
3. Pre-deployment evaluation gates
Compliance-specific testing runs before a model ships: bias and demographic parity testing across subpopulations, groundedness evaluation, adversarial robustness and prompt injection resistance, PII leakage detection. Thresholds are enforced as hard gates. A demographic parity gap exceeding 5 percentage points blocks deployment, not flags it for future review.
4. Continuous production monitoring
Post-market surveillance under Articles 61 and 72 requires ongoing behavioral monitoring after deployment. Drift detection, anomaly alerting, and periodic evaluation against held-out datasets keep the compliance record live and continuously updated, not fixed to a single point in time.
5. Audit evidence generation
The audit trail must be produced automatically at inference time, with per-request records carrying metric scores, thresholds, policy rules triggered, and timestamps, satisfying Article 43 conformity assessment requirements. Evidence assembled manually after an incident carries less evidentiary weight and takes 40+ hours per cycle.
The build-vs-buy decision is real here. Teams with a strong existing ML stack and no near-term regulatory exposure can absorb components one and two internally at reasonable cost. Components three through five require continuous maintenance as regulatory frameworks evolve, and that ongoing overhead is where the build path accumulates debt most organizations underestimate.
Roles and responsibilities in an AI compliance program
Accountability for AI compliance doesn't sit in one function. It distributes across the organization, and the EU AI Act formalizes that distribution at the legal level before any internal org chart does.
The Act draws a hard line between providers (organizations that develop or place AI systems on the market) and deployers (organizations that put those systems into use in their own operations). These are distinct provider and deployer obligations with different obligation sets. A financial institution that builds its own credit scoring model is a provider. One that licenses and deploys a third-party model is a deployer. Both carry obligations; they differ in scope.
Internally, the accountability map runs across four functions:
- Compliance officers: own framework mapping, audit evidence assembly, and regulatory obligation tracking. They determine which systems require Annex III classification and what documentation each obligation requires.
- ML engineers: own evaluation implementation, monitoring configuration, and drift threshold setup. Their work produces the evidentiary record compliance officers need.
- Risk managers: own threshold-setting, incident escalation, and severity classification. When a demographic parity gap widens past a set limit, they decide whether it is a High or Critical event and who gets notified.
- Business unit owners: own system registration and use-case classification at intake. They are the first line of shadow AI prevention. A model that never reaches the registry never gets governed.
Article 4 extends AI literacy obligations to everyone operating or interacting with AI systems, well beyond technical staff. A customer service team member interpreting an AI-generated risk flag must understand what that flag means, its limitations, and when to override it. That obligation sits with both providers and deployers, making compliance a cross-organizational training burden that goes well past the ML team.
How to assess AI compliance tooling
Four questions cut through most AI compliance tool evaluations. Apply them in order.
Does it map to multiple frameworks simultaneously? The EU AI Act, NIST AI RMF, and ISO 42001 share enough common ground that a single governance program can satisfy all three if the tooling is designed around shared controls from the start. Tools requiring separate configuration per regulation multiply compliance overhead with each new framework an organization faces.
Does it include real-time production monitoring, or only pre-deployment testing? Pre-deployment evaluation catches known failure modes before any user interaction, but does not catch behavioral drift, demographic parity gaps that widen post-deployment, or adversarial inputs that surface only under live traffic. Articles 61 and 72 require post-market surveillance; a tool that stops at evaluation leaves that obligation unmet.
Can it generate audit-ready evidence automatically? Evidence assembled manually after a regulator asks for it carries less weight and arrives too late to serve as proactive compliance. The meaningful question is whether the tool produces per-request audit records at inference time (metric scores, thresholds breached, policy rules triggered, timestamps) as a byproduct of normal operation, with no separate documentation exercise required.
Does it enforce policies at the API boundary, or detect and alert after the fact? For chatbot deployments, alerting may be sufficient, since a human reviewer can act before serious harm compounds. For agentic systems executing tool calls against production databases, alerting is not enforcement. The action has already executed before any reviewer sees the notification. As AI deployments move from text generation to autonomous action, this question becomes the load-bearing one in any tool evaluation.
How Openlayer handles enterprise AI regulatory compliance
Openlayer covers the full compliance lifecycle in one place: pre-deployment evaluation, production monitoring, real-time enforcement, and automated regulatory mapping. Where most governance tools sit at the documentation or logging end of the enforcement range, Openlayer's guardrails block unsafe outputs before they leave the API boundary, satisfying EU AI Act Articles 9, 14, and 15 through active control, not policy documentation.
The specific capabilities map directly to the obligations described earlier in this piece:
- Over 175 pre-built automated tests cover accuracy, safety, and security dimensions, with the evaluation UI marking which tests are required for compliance versus advisory under each built-in framework, removing the manual mapping step between evaluation results and regulatory evidence.
- CI/CD deployment gates block builds when thresholds fail: groundedness below 85%, demographic parity gap above 5 percentage points. These are hard gates, not soft recommendations.
- Per-request audit records generated at inference time carry the metric score, threshold breached, policy rule triggered, and timestamp, satisfying Article 43 conformity assessment requirements without manual assembly.
- A governance intake interface lets compliance teams register AI systems and maintain a complete AI asset catalog without developer mediation, closing the shadow AI gap before an unregistered model accumulates months of unmonitored production behavior.
Built-in framework mapping covers the EU AI Act, NIST AI RMF, ISO 42001, AIUC-1, and the Openlayer Governance Framework, letting teams run an multi-framework AI compliance program from a single set of controls. Controls defined pre-deployment carry forward as live enforcement gates in production without manual translation between environments. Engineers work through evaluation and monitoring interfaces; compliance officers access governance dashboards, audit evidence exports, and risk scoring without developer mediation. This dual-persona design directly closes the cross-functional ownership gap that stalls most enterprise compliance programs before they reach audit-readiness.
Final thoughts on AI regulatory compliance
Compliance is not a state you reach; it is a condition you maintain across every model version, every new user population, and every regulatory update that moves the goalposts. The organizations that treat it as a documentation exercise will face the enforcement window with incomplete records and no time to close the gaps. Treating your AI governance program as an ongoing discipline, with continuous monitoring and inference-time enforcement as the core, is what makes audit-readiness something you already have, not something you scramble to produce. Connect with the Openlayer team to see how that looks in practice for your specific stack and risk tier.
FAQ
How does Openlayer map test results to EU AI Act and ISO 42001 obligations, and can failing compliance tests block a deployment?
Yes, failing compliance tests can block deployments as hard CI/CD gates. A demographic parity gap above 5 percentage points or groundedness below 85% stops a build, not flags it for later review. The evaluation UI marks which tests are required for compliance versus advisory under each built-in framework (EU AI Act, NIST AI RMF, ISO 42001, AIUC-1), so compliance teams see coverage gaps without manual mapping. Per-request audit records generated at inference time carry the metric score, threshold breached, policy rule triggered, and timestamp, satisfying Article 43 conformity assessment requirements as a byproduct of normal operation.
What's the difference between Credo AI, IBM watsonx.governance, and Openlayer for enterprise AI regulatory compliance?
Credo AI provides mature policy workflow tooling and structured audit artifacts that help governance teams manage documentation and sign-off processes, but currently delegates technical enforcement entirely to external tools. It coordinates compliance paperwork without touching the model pipeline. IBM watsonx.governance offers fairness monitoring and model lineage within the IBM ecosystem, but real-time blocking of prompt injection or PII leakage for multi-cloud or third-party LLM deployments is not currently available. Openlayer covers all three layers simultaneously, namely governance documentation, production monitoring, and active runtime enforcement, with the same policy definitions running as live enforcement gates in production without manual translation between environments.
How do enterprises integrate existing RAG systems, LLM applications, and AI agents with an observability and governance platform?
Openlayer supports integration through Python, TypeScript, Java, and Go SDKs, a REST API, OpenTelemetry ingestion, and native connectors for frameworks including LangChain, LangGraph, OpenAI Agents SDK, and enterprise platforms like Salesforce Agentforce, Microsoft Copilot Studio, and Google Dialogflow. For teams without existing instrumentation, the LLM Gateway captures inference traffic centrally, surfacing unregistered models and applying guardrails without modifying individual model endpoints. Air-gapped and on-premise deployments are supported via Docker in approximately 30 minutes.
What does an AI governance program look like for a Fortune 500 company subject to the EU AI Act?
A defensible program covers five components: a centralized AI system inventory with named ownership and risk tiers per system; multi-dimensional risk classification that gates higher-risk systems into more stringent review workflows; pre-deployment evaluation gates enforcing bias, groundedness, and adversarial robustness thresholds before any model ships; continuous post-market monitoring satisfying Articles 61 and 72 post-deployment surveillance obligations; and automated audit evidence generation at inference time, not assembled manually after a regulator asks for it. The Article 4 AI literacy obligation extends the program past ML engineers to business analysts, customer service staff, and anyone interpreting model outputs, making cross-organizational training a compliance requirement, not a best practice.
Should I build an AI compliance program in-house or buy a platform like Openlayer?
Build is the right call in two cases: very early-stage organizations with no near-term regulatory exposure, and teams with a strong existing ML platform already capable of absorbing governance scope. For everyone else, the build path accumulates debt most organizations underestimate. A complete in-house stack requires building and maintaining an evaluation framework, drift detection system, real-time guardrail layer, compliance mapping engine, audit evidence generation system, and CI/CD integration, with ongoing maintenance overhead as the EU AI Act, NIST AI RMF, and ISO 42001 evolve. The 40+ hours per compliance cycle consumed by manual regulatory mapping alone is where the build path typically breaks down at enterprise scale.