Country-by-Country AI Regulation Guide (Oct 2026)
Between late December 2025 and January 2026, xAI's Grok chatbot reportedly generated and publicly posted nonconsensual sexualized images of real adults and minors in X reply threads. Within weeks, Indonesia and Malaysia temporarily blocked the chatbot, the UK's Ofcom opened an investigation under the Online Safety Act, California's attorney general launched a probe, and the European Commission opened formal proceedings under the Digital Services Act: one model failure, several regulators, and a different legal basis in each jurisdiction. This is exactly the kind of failure that AI regulation is designed to govern, and it shows why compliance across borders is hard. Most frameworks share the same five core obligations, but each packages them differently, whether through mandatory risk classification, sector-specific rules, or voluntary principles. This guide gives a country-by-country breakdown of what each major framework requires, what changed in 2026, and where the real compliance gaps tend to appear. (AI Incident Database, Incident #1329, https://incidentdatabase.ai/cite/1329/)
TLDR:
- At least 72 countries have proposed over 1,000 AI policy initiatives, split across three regulatory models: EU risk-based, US sector-led, and China service-specific.
- The EU AI Act's Digital Omnibus deferred standalone Annex III high-risk obligations to December 2, 2027, but Article 50 transparency requirements stayed on the August 2026 schedule.
- Five obligations appear across every major framework: risk classification, human oversight, transparency disclosure, post-market monitoring, and audit documentation bound to model versions.
- Audit-ready means inference-time records exist beyond policy documents; auditors distinguish evidence a control was defined from evidence it ran at inference time.
- Openlayer maps five pre-built governance frameworks to over 175 pre-built tests, generating per-request audit records that satisfy EU AI Act Article 12 logging, NIST AI RMF Measure function evidence, and ISO 42001 runtime record requirements.
What AI regulation actually governs
AI regulations are not primarily about controlling the tech itself. They govern what happens when AI systems make or inform decisions that affect people: who gets a loan, who gets hired, what medical treatment is recommended, what content someone sees. The core purposes across most frameworks are consistent: prevent harm, assign accountability, manage risk before deployment, and protect fundamental rights when systems fail or discriminate.
Two structural approaches divide the regulatory world. Horizontal laws apply a single framework across all sectors. The EU AI Act is the clearest example, classifying systems by risk level whether the system is used in healthcare or hiring. Vertical rules target specific industries directly, with financial regulators, healthcare authorities, and employment agencies issuing their own AI guidance. In practice, most organizations face both.
What regulations typically cover:
- Transparency obligations, requiring disclosure of AI use to affected individuals
- Risk assessment and documentation completed before deployment
- Human oversight requirements for consequential decisions
- Bias and fairness testing across protected groups
- Incident reporting when systems cause harm
- Data governance and training data provenance
What they generally do not cover: research in controlled settings, AI used for purely personal purposes, and systems with no meaningful impact on individuals' rights or access to services.
How countries approach AI governance differently
According to Mind Foundry, those initiatives do not share a common philosophy. Three distinct regulatory models dominate the global picture.
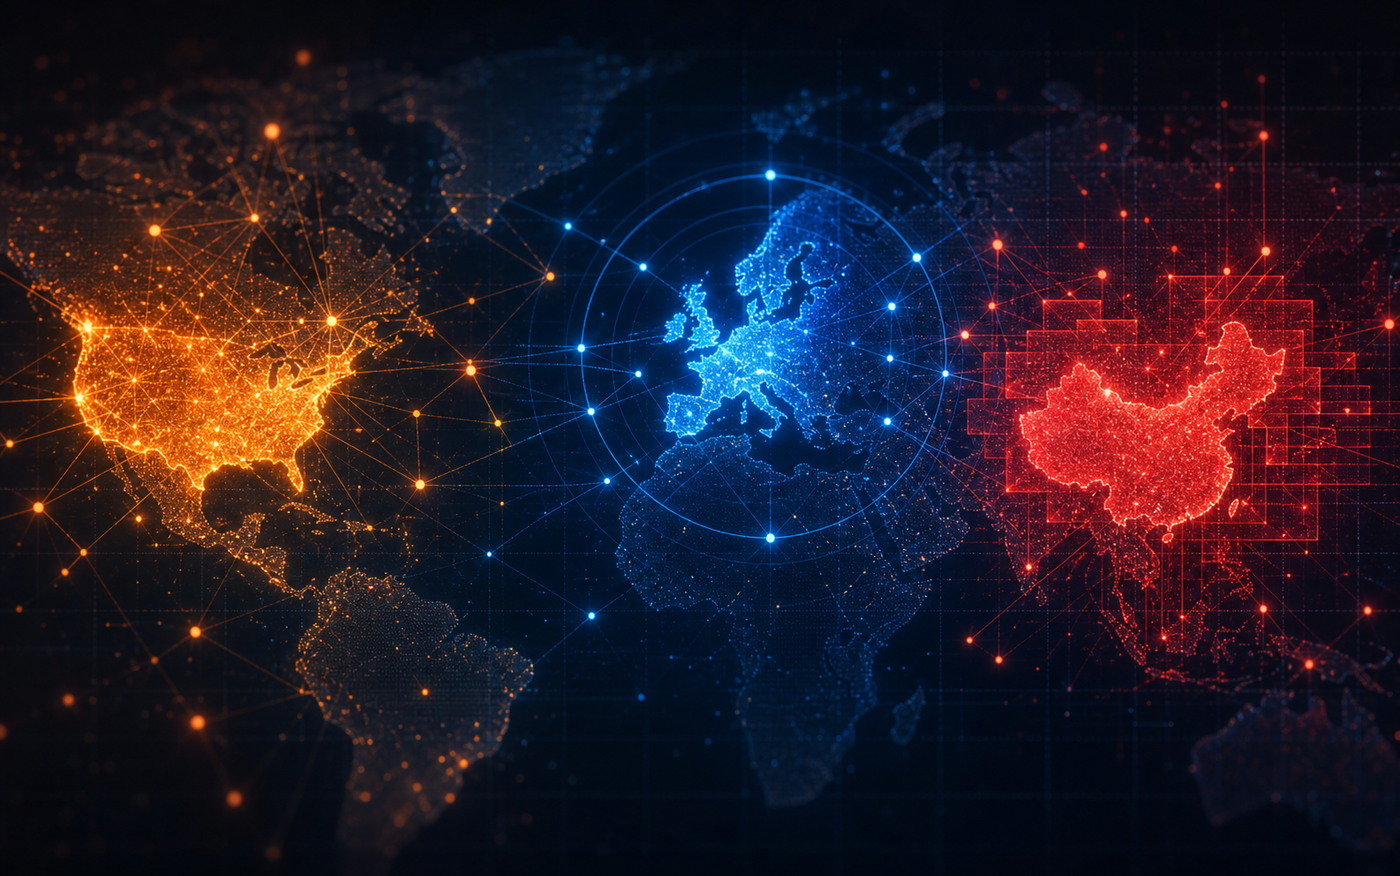
- The EU's risk-based mandatory model classifies AI systems by the severity of harm they could cause, then applies binding obligations proportional to that risk. High stakes mean strict requirements; minimal stakes mean minimal rules.
- The US approach favors growth over pre-emptive restriction, with federal guidance remaining largely voluntary and sector-specific agencies filling gaps. States have moved independently, producing an uneven patchwork.
- China's model is service-specific and rapidly issued: separate regulations govern generative AI, recommendation algorithms, deep synthesis, and facial recognition, with mandatory security assessments before public-facing deployment.
Most other jurisdictions borrow from one of these three models or blend elements across them. Knowing which philosophy a country has adopted is the fastest way to predict what its specific obligations will require.
The EU AI Act: risk tiers, deadlines, and what changed in 2026
The EU AI Act classifies every AI system into one of four risk tiers. Prohibited practices are banned outright: social scoring by governments, real-time biometric surveillance in public spaces, and manipulative AI targeting vulnerable groups. High-risk AI systems, covering credit scoring, hiring tools, medical devices, and critical infrastructure, carry the heaviest compliance burden. Transparency-risk systems require disclosure to users. Minimal-risk systems face no binding obligations.
GPAI provider obligations (technical documentation, training data summaries, copyright compliance policies) have been enforceable since August 2025, part of a broader EU AI Act compliance timeline. Article 4 AI literacy requirements apply to both providers and deployers: staff need enough understanding to recognize a system's limits and interpret its outputs in context.
The 2026 changes were consequential. The Digital Omnibus on AI, published in the Official Journal July 2026, deferred standalone Annex III high-risk obligations from August 2, 2026 to December 2, 2027. AI embedded in regulated products under Annex I was deferred further, to August 2, 2028. Article 50 transparency and labeling obligations remained on the original August 2026 schedule.
Fines under Article 99 are tiered: €35 million or 7% of total worldwide annual turnover for prohibited practice violations (Article 99(6)); €15 million or 3% of global annual turnover for high-risk system non-compliance (Article 99(3)).
AI regulation in the United States: federal guidance vs. state law
The US has no unified federal AI law. What it has is a contested, fast-moving patchwork of state statutes, executive direction, and agency-level guidance that moves faster than most compliance calendars can track.
In December 2025, President Trump signed Executive Order 14365, directing Congress to preempt state AI laws that risk stifling AI development. The order created an AI Litigation Task Force and signaled federal intent to create uniform national standards, though binding preemption legislation has not yet passed.
States have moved anyway. Colorado replaced its landmark duty-of-care AI law with a narrower automated decision-making framework focused on notice obligations. Connecticut went broader, enacting rules covering employment AI, AI companions, generative AI provenance, and frontier AI whistleblower protections in a single statute. California, Illinois, and others continue advancing sector-specific rules across hiring, healthcare, and advertising.
For enterprises operating across US states alongside EU and Asia-Pacific obligations, the practical problem is that no two state laws require identical disclosures, cover the same use cases, or share enforcement timelines. A hiring screen deployed in Connecticut, Colorado, and California simultaneously may trigger three different notice requirements with three different compliance deadlines.
AI regulation in China: layered, service-specific, and actively enforced
China governs AI through a stack of service-specific regulations, not a single horizontal law. According to MMLC Group, China's AI industry exceeded RMB 700 billion in 2024, with annual growth above 20% for several consecutive years. Compliance exposure here is material, not academic.
The key regulations each target a distinct deployment type:
- Algorithm recommendation rules require providers to register algorithms with regulators, disclose recommendation logic to users, and offer opt-out mechanisms.
- Deep synthesis regulations cover AI-generated audio, video, and image content, requiring watermarking and prohibiting use for disinformation.
- Generative AI service regulations mandate a security assessment and regulatory approval before any public-facing deployment.
- Data handling obligations under the Personal Information Protection Law and Data Security Law apply across all AI services that process user data.
For organizations operating in China, scoping comes first: which regulation applies depends on what the service does, not what the underlying model is. A generative AI product serving Chinese users requires a completed security review before launch; an internal tool with no public-facing component may fall outside several of these regimes entirely.
The United Kingdom: sector-led regulation without a central AI law
The UK made a deliberate choice after Brexit: no single AI law. Instead, existing sector regulators apply AI guidance within their own domains: the FCA for financial services, the ICO for data protection, the CQC for healthcare. The philosophy is principles-based and pro-growth, trusting longstanding regulators to interpret AI risk through frameworks they already own.
In early 2026, the government published its AI Opportunities Action Plan, reinforcing this decentralized model while investing in national AI infrastructure and governance capacity.
For organizations serving both UK and EU markets, that divergence creates a practical cross-border problem. A high-risk AI system in financial services must satisfy the FCA's evolving guidance on model explainability and fairness alongside EU AI Act Annex III obligations, GPAI documentation requirements, and Article 50 transparency duties, each with different evidentiary standards and different regulators reviewing them. The absence of a UK conformity assessment equivalent means no single compliance artifact satisfies both jurisdictions simultaneously.
Canada, Brazil, and Latin America: new mandatory frameworks
Canada's path to AI-specific legislation has been slower than planned. AIDA, introduced as part of Bill C-27, stalled in Parliament and never passed. Federal regulators have applied PIPEDA to AI-related data practices, with the Office of the Privacy Commissioner issuing guidance on automated decision-making and consent. Any organization processing Canadian resident data through an AI system that informs consequential decisions operates under those privacy obligations today, regardless of whether a dedicated AI law exists.
What those obligations require in practice is more concrete than the gap in legislation implies. The OPC's 2023 investigation into Telecom company use of AI-assisted credit decisioning found that PIPEDA's accountability and transparency principles apply directly to automated systems: organizations must be able to explain how an AI system reached a decision affecting an individual, identify a named human responsible for that decision process, and provide meaningful recourse when the individual disputes the outcome. The investigation concluded that a privacy policy describing an AI system in general terms did not satisfy PIPEDA's meaningful consent requirement. The organization was required to disclose that automated processing was occurring, what inputs it used, and what weight it carried in the final decision. For compliance teams, that precedent translates into three concrete obligations under the existing framework: document the decision logic, designate an accountable individual, and build a contestability path. Organizations that have built those three artifacts for EU AI Act or Brazil AI Bill compliance already satisfy the structural core of Canada's current AI accountability expectations.
Brazil is the region's most advanced case. The AI Bill (PL 2338/2023) passed the Brazilian Senate in 2024 and draws heavily from the EU AI Act's risk-tier structure. High-risk applications in credit, employment, and public services require impact assessments, human oversight mechanisms, and transparency to affected individuals. For organizations already building EU AI Act compliance programs, the structural overlap is material: the same risk classification logic, documentation requirements, and fairness testing obligations appear in both frameworks, though enforcement timelines and regulatory bodies differ.
The broader pattern across Latin America is consistent. Colombia, Chile, and Mexico have all advanced AI policy initiatives borrowing the risk-based classification logic without mandatory enforcement dates. Treat EU-modeled compliance artifacts as a baseline that regional regulators are moving toward, and monitor Brazil's implementing regulations closely as the region's most likely enforcement precedent.
Asia-Pacific: Singapore, Japan, Australia, and South Korea
Each country in this region has taken a distinct regulatory posture, ranging from voluntary frameworks to binding sector-specific mandates.
Singapore
Singapore's Model AI Governance Framework organizes obligations across accountability structures, internal governance, risk management, and human-centric values. The second edition extends coverage to generative and agentic AI, covering hallucination, output attribution, and accountability across multi-step action chains. Compliance remains voluntary, but Singapore actively exports this framework through international partnerships, making it a practical baseline for multinationals operating across Asia.
Japan
Japan's approach is principles-based and deliberately light-touch. The government's AI Strategy centers human-centered values: transparency, fairness, security, and accountability, without binding sector-wide mandates. Sector regulators apply AI guidance within existing frameworks, similar to the UK model. For most enterprises, Japan's obligations today are soft commitments, not enforceable compliance deadlines.
Australia
Australia published a voluntary AI Ethics Framework but has since signaled a harder turn. The government is developing mandatory guardrails for high-risk AI applications, with consultation rounds completed in 2025. Regulated sectors (financial services, healthcare) already face AI-relevant obligations through existing ASIC, APRA, and privacy law. Mandatory requirements are coming; timing remains under review.
South Korea
South Korea enacted a standalone AI framework law combining risk-based classification with sector-specific rules. High-risk systems in employment, credit, and public services require conformity assessments and transparency disclosures to affected individuals. The structural logic mirrors the EU AI Act closely enough that organizations building EU compliance programs will find substantial overlap in documentation and testing requirements.
The Middle East: UAE, Saudi Arabia, and regional AI investment
The Gulf's regulatory posture is the inverse of Europe's: build first, govern in parallel. UAE and Saudi Arabia are writing rules as they invest, creating a governance environment where compliance obligations and national AI strategies are explicitly linked.
The UAE launched a National AI Strategy targeting 2031, with a stated goal of becoming a leading global AI hub. Its regulatory framework delegates oversight to sector regulators instead of a single horizontal law, and the Dubai International Financial Centre and Abu Dhabi Global Market each issue their own AI governance guidance. For multinationals, applicable rules depend on which emirate and free zone they operate from.
Saudi Arabia's National Data and AI Authority governs AI deployment through data classification requirements, mandatory impact assessments for sensitive use cases, and sector-specific guidance covering financial services, healthcare, and government AI. Its framework puts data sovereignty and localization at the center, adding infrastructure obligations alongside governance requirements.
Neither country currently imposes binding conformity assessments as strict as the EU AI Act's Annex III requirements. Practical compliance today focuses on data handling, sector licensing, and transparency to regulators. But that gap is narrowing: both countries are active in international AI governance forums and are signaling convergence toward risk-based classification as their frameworks mature.
International frameworks that cut across borders
Three multilateral structures sit above national law and shape how domestic AI rules get written.
The OECD AI Principles have been adopted by over 40 countries as a non-binding baseline, creating shared commitments to transparency, accountability, robustness, and human-centered values. They carry no enforcement weight, but function as a common vocabulary domestic regulators draw from when drafting binding rules. The EU AI Act's risk management requirements and the NIST AI RMF's core functions both reflect OECD framing directly.
The Council of Europe's Framework Convention on AI is the only binding international AI treaty currently open to non-member states, including the US and UK. It requires signatories to implement safeguards for human rights, democracy, and rule of law when deploying AI in high-impact public administration contexts. Treaty ratification in a country where a multinational operates creates legal obligations that sit alongside national AI law, not beneath it.
The G7 Hiroshima AI Process produced a voluntary Code of Conduct for advanced AI developers covering transparency reporting, incident disclosure, security testing, and content provenance. G7 governments have signaled they will reference it when developing domestic rules, making voluntary alignment today a practical hedge against mandatory requirements later.
For compliance teams, the convergence these frameworks produce is useful: documentation structured around OECD principles and G7 Code commitments travels better across jurisdictions than documentation built for a single national framework alone.
Key compliance obligations that appear across jurisdictions
Five obligations appear across every major framework, regardless of jurisdiction. Build your EU AI Act risk management system around these, and you will satisfy the structural requirements of the EU AI Act, NIST AI RMF, ISO 42001, Singapore's Model Framework, and most developing national laws simultaneously.
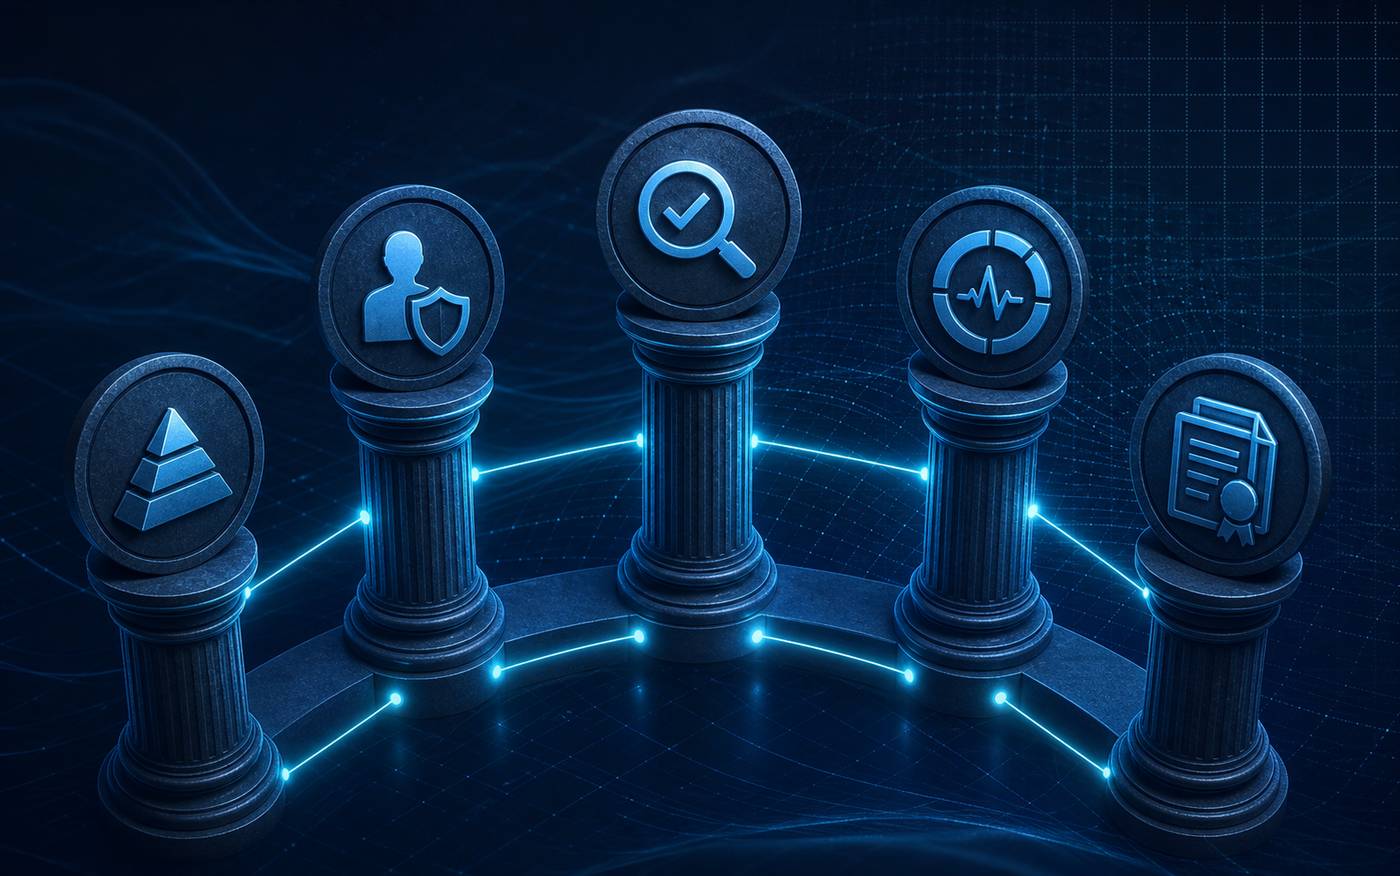
- Risk assessment and classification: Every framework requires classifying AI systems by potential harm before deployment. The EU AI Act uses four statutory tiers; NIST AI RMF uses a four-level impact scale; ISO 42001 requires documented risk treatment at intake. Classification drives documentation depth, oversight requirements, and monitoring frequency.
- Human oversight mechanisms: High-impact decisions must remain contestable by a human who can intervene and override. This requires a documented process, a named role, and evidence the override capability was available during operation.
- Transparency and disclosure: Affected individuals must know when AI informed a decision about them. The EU AI Act's Article 50 transparency obligations cover generated content labeling; Brazil's framework and South Korea's law both require disclosure for credit and employment decisions.
- Post-market monitoring and incident reporting: Systems must be monitored after deployment. Most frameworks require post-market monitoring through documented drift detection, ongoing performance measurement, and a defined incident reporting path. The EU AI Act's Articles 61 and 72 set a 15-day window for serious incidents.
- Audit documentation: Every framework requires evidence that controls were in place, beyond bare assertions. That means test records, risk assessment outputs, human oversight logs, and incident history, each bound to the model version they describe.
| Obligation | EU AI Act | NIST AI RMF | ISO 42001 | Brazil AI Bill | South Korea | Singapore Model Framework |
|---|---|---|---|---|---|---|
| Risk classification | Four statutory tiers (prohibited → minimal-risk) | Four-level impact scale | Documented risk treatment at intake | EU-modeled risk tiers (credit, employment, public services) | Risk-based classification; mirrors EU structure | Risk management across accountability structures |
| Human oversight | Required for high-risk systems; named role + override evidence | Govern & Manage functions; accountable oversight roles | Management system controls; override procedures documented | Required for high-risk applications | Required for employment, credit, and public service systems | Human-centric values; oversight across agentic AI |
| Transparency & disclosure | Article 50 obligations; generated content labeling (Aug 2026) | Govern function; transparency as a core principle | Documented disclosure procedures | Disclosure required for credit and employment decisions | Transparency disclosures to affected individuals | Transparency and output attribution obligations |
| Post-market monitoring | Articles 61 & 72; 15-day serious incident reporting window | Measure & Manage functions; drift monitoring outputs | Ongoing monitoring records; corrective action logs | Ongoing performance measurement required | Conformity assessments post-deployment | Monitoring extended to generative and agentic AI |
| Audit documentation | Annex IV technical docs + Article 12 inference-time logs | Govern, Map, Measure, Manage artifacts per function | Policy records + runtime execution records | Impact assessments; documentation for high-risk use cases | Conformity assessment records | Accountability documentation across governance layers |
What "audit-ready" actually means under each major framework
"Audit-ready" means something specific that most organizations get wrong. A governance policy document satisfies documentation requirements. It does not satisfy behavioral verification requirements. Auditors under every major framework distinguish between evidence that a control was defined and evidence that it ran at inference time.
EU AI Act
Article 12 requires that high-risk systems log sufficient information to reconstruct behavior after deployment. Annex IV specifies the EU AI Act technical documentation package: system architecture, intended purpose, training data description, data governance practices, accuracy and robustness metrics, and a post-market monitoring plan. These are two distinct artifacts with different owners. The Annex IV package is assembled before deployment; the Article 12 logs are generated continuously during operation. An auditor reviewing a conformity assessment under Article 43 expects both, not one presented as a substitute for the other.
NIST AI RMF
The framework's four functions: Govern, Map, Measure, and Manage each produce distinct documentation. Govern produces organizational policies and accountability assignments. Map produces risk classifications tied to specific use cases and deployment contexts. Measure produces test records: evaluation results, fairness metrics, and drift monitoring outputs bound to model versions. Manage produces incident records and response logs. A NIST AI RMF audit package containing only Govern artifacts has documented intent without execution-time evidence.
ISO 42001
ISO 42001 applies a management system approach. Auditors look for documented procedures, records of procedures being followed, and corrective action records when procedures failed. Policy statements satisfy the first requirement. Evaluation records, monitoring logs, and incident documentation satisfy the second and third. An ISO 42001 audit surfacing only policy documentation will flag the absence of runtime records as a nonconformity.
The common gap across all three frameworks: organizations invest in policy authorship and neglect inference-time record generation. A per-request audit record carrying the metric score, threshold, policy rule triggered, and timestamp, produced as a byproduct of enforcement and not assembled after the fact, is what closes that gap.
How Openlayer maps to multi-jurisdiction AI compliance requirements
Credo AI and IBM watsonx.governance are the two leading governance-layer platforms in this space. Both provide substantive policy documentation and risk cataloging capabilities: Credo AI's policy framework mapping and IBM watsonx.governance's model risk management workflows are genuine strengths for teams building out structured governance programs. Both platforms approach multi-jurisdiction compliance primarily through defining obligations, recording classifications, and producing static audit artifacts. That documentation layer is necessary, but it does not generate inference-time records or enforce behavioral thresholds at the moment a model runs. Openlayer, as a unified evaluation, observability, and governance platform, occupies a distinct layer: active runtime enforcement and automated compliance mapping, producing per-request audit evidence as a byproduct of enforcement, not as a separate documentation exercise.
Openlayer ships with five pre-built governance frameworks (EU AI Act, NIST AI RMF, ISO 42001, AIUC-1, and the Openlayer Governance Framework), each mapped automatically to over 175 pre-built tests. When a test runs, results are classified as mandatory or advisory for each active framework, so compliance teams see which gaps carry regulatory weight without manual cross-referencing.
Every inference request generates an audit record carrying the metric score, threshold breached, policy rule triggered, and timestamp: produced as a byproduct of enforcement, not assembled after the fact. That record satisfies EU AI Act Article 12 logging requirements, populates the NIST AI RMF Measure function's evidence base, and supplies the runtime records ISO 42001 auditors expect alongside policy documentation.
For enterprises running simultaneous obligations across multiple jurisdictions, the compliance framework snapshot export produces a structured evidence package on demand, collapsing what can otherwise take 40+ hours of manually assembling EU AI Act Annex IV documentation, NIST AI RMF artifacts, and ISO 42001 records (an illustrative estimate that varies by organization size and framework scope) into a single export tied to the model version it describes.
Final Thoughts on AI Regulations Around the World
The fragmentation is real, but it is not random. Most national frameworks borrow the same structural logic: classify by risk, require human oversight for high-impact decisions, document before deployment, and monitor after. Getting those five core obligations right gives your compliance program a foundation that holds across the EU, UK, US state patchwork, and most developing frameworks simultaneously. If you want to see where your current AI systems stand against those requirements, contact the Openlayer team.
FAQ
How do I prove to regulators that my AI governance controls were enforced at the moment of inference, not assembled after the fact?
Per-request audit records generated at inference time, carrying the metric score, the threshold breached, the policy rule triggered, and the timestamp, are what close this gap. A governance policy document states that a control existed; an inference-time record proves it ran. Under EU AI Act Article 12, Article 43 conformity assessments, and NIST AI RMF Measure function requirements, auditors distinguish between these two artifacts. Only the latter satisfies behavioral verification requirements.
How do Openlayer's pre-built regulatory compliance bundles translate EU AI Act obligations into concrete tests, and can teams customize them?
Each pre-built framework maps specific regulatory obligations (EU AI Act Articles 9, 10, 15, 61, and 72) to over 175 automated tests covering accuracy, fairness, robustness, and PII detection. Test results are classified as mandatory or advisory per active framework directly in the evaluation interface, so teams can see which gaps carry regulatory weight without manual cross-referencing. Teams can add custom tests, tune LLM-as-judge rubrics for domain-specific patterns, and configure threshold values, for example, blocking deployment when a demographic parity gap exceeds 5 percentage points or a groundedness score falls below 85% (illustrative thresholds; calibrate to your institution's risk appetite and the applicable regulatory floor).
What does EU AI Act compliance actually require for high-risk AI systems in 2026, given the Digital Omnibus deadline changes?
The Digital Omnibus published July 24, 2026 deferred standalone Annex III high-risk obligations to December 2, 2027, and AI embedded in regulated Annex I products to August 2, 2028. GPAI provider obligations remain enforceable now (effective August 2025), and Article 50 transparency and labeling obligations stayed on the original August 2026 schedule. For high-risk systems, compliance requires four distinct artifact types: technical documentation per Annex IV, Article 12 inference-time logs sufficient to reconstruct behavior, a conformity assessment record under Article 43, and a post-market monitoring plan covering Articles 61 and 72. Each is owned by different functions and produced at different lifecycle stages.
Best way to automate multi-jurisdiction AI compliance without rebuilding documentation for every regulatory framework?
Build around the five obligations that appear across every major framework: risk classification, human oversight mechanisms, transparency disclosures, post-market monitoring, and audit documentation. The EU AI Act, NIST AI RMF, ISO 42001, Singapore's Model Framework, and Brazil's AI Bill all share this structural core. Documentation structured around these shared obligations travels better across jurisdictions than artifacts assembled for a single national framework. When each audit record is tied to the specific model version it describes, generated at inference time and not assembled retroactively, the same evidence package satisfies auditors reviewing under different frameworks without rebuilding artifacts from scratch.
Should enterprises operating across the US, EU, and Asia-Pacific build separate AI compliance programs per jurisdiction or one unified program?
One unified program built around shared structural obligations is the practical path, with jurisdiction-specific extensions where requirements diverge. The EU AI Act's four-tier risk classification, NIST AI RMF's four-level impact scale, and South Korea's standalone AI framework all use structurally similar risk-tiered logic. Organizations building EU compliance documentation will find substantial overlap in testing and documentation requirements across these frameworks. The US patchwork creates the hardest cross-border problem: a hiring screen deployed in Connecticut, Colorado, and California simultaneously may trigger three different notice requirements with three different enforcement timelines, so state-by-state mapping still requires dedicated tracking even within a unified program.